Metal Card RFID Technology Types
High-security AES Metal RFID Cards
High-security AES HF is the secure end of the 13.56 MHz family: AES-128 cryptography, 2K, 4K, or 8K of memory, and a file system that lets one card carry several independent applications — door access, cashless spend inside a venue, print release — each with its own keys. Current estates specify a recent generation, and the integrator, not the card maker, defines the application map.
(01) — Route brief
Match the chip, data, and approval path before choosing the finish.
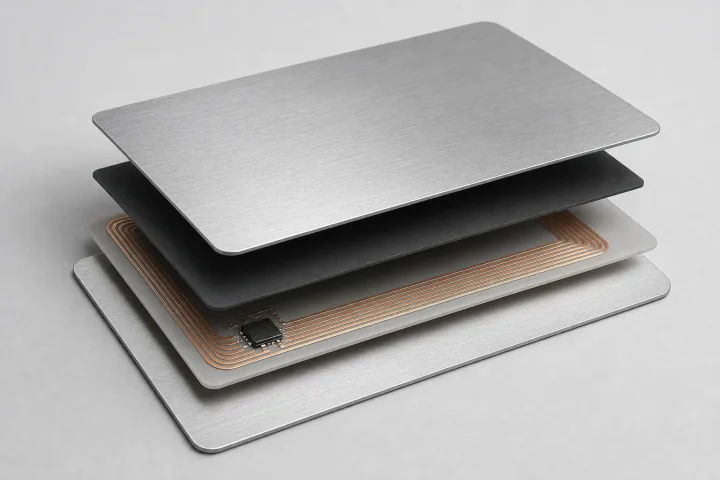
This is the production brief for High-security AES: what it is for, how it behaves, what needs encoding, and what must pass before the batch starts.
(02) — Visual references
Compare the details that change the finished card.
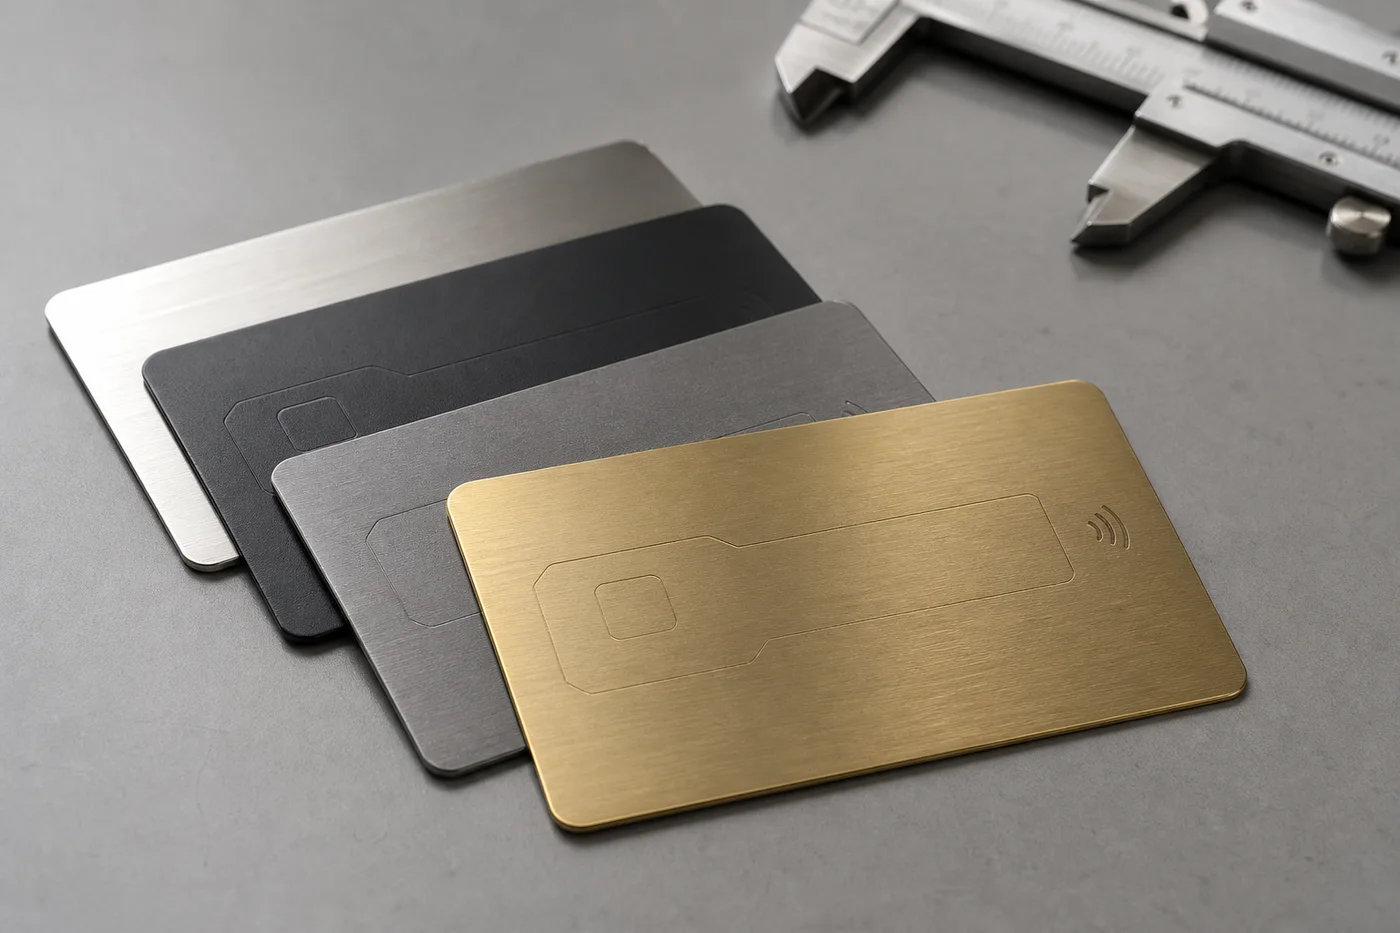
Use this board to read the essentials at a glance: metal finish, marking contrast, edge quality, reader fit, and presentation style.
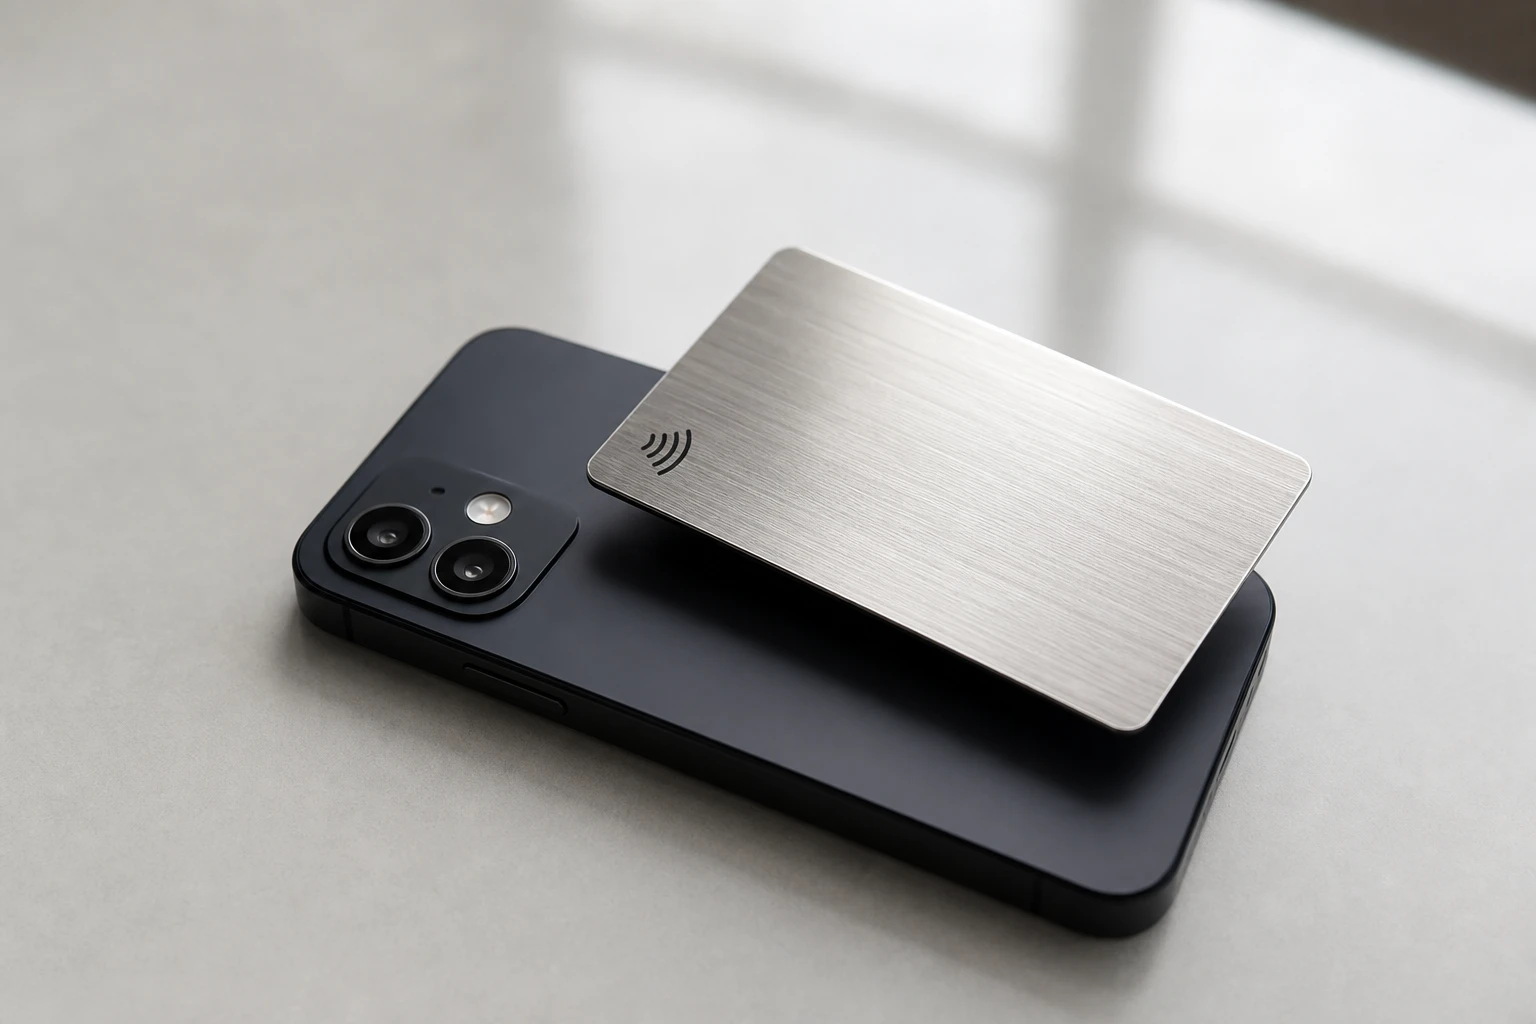
A brushed stainless route for phone-readable NFC, NDEF URLs, profiles, menus, loyalty, and public tap experiences.
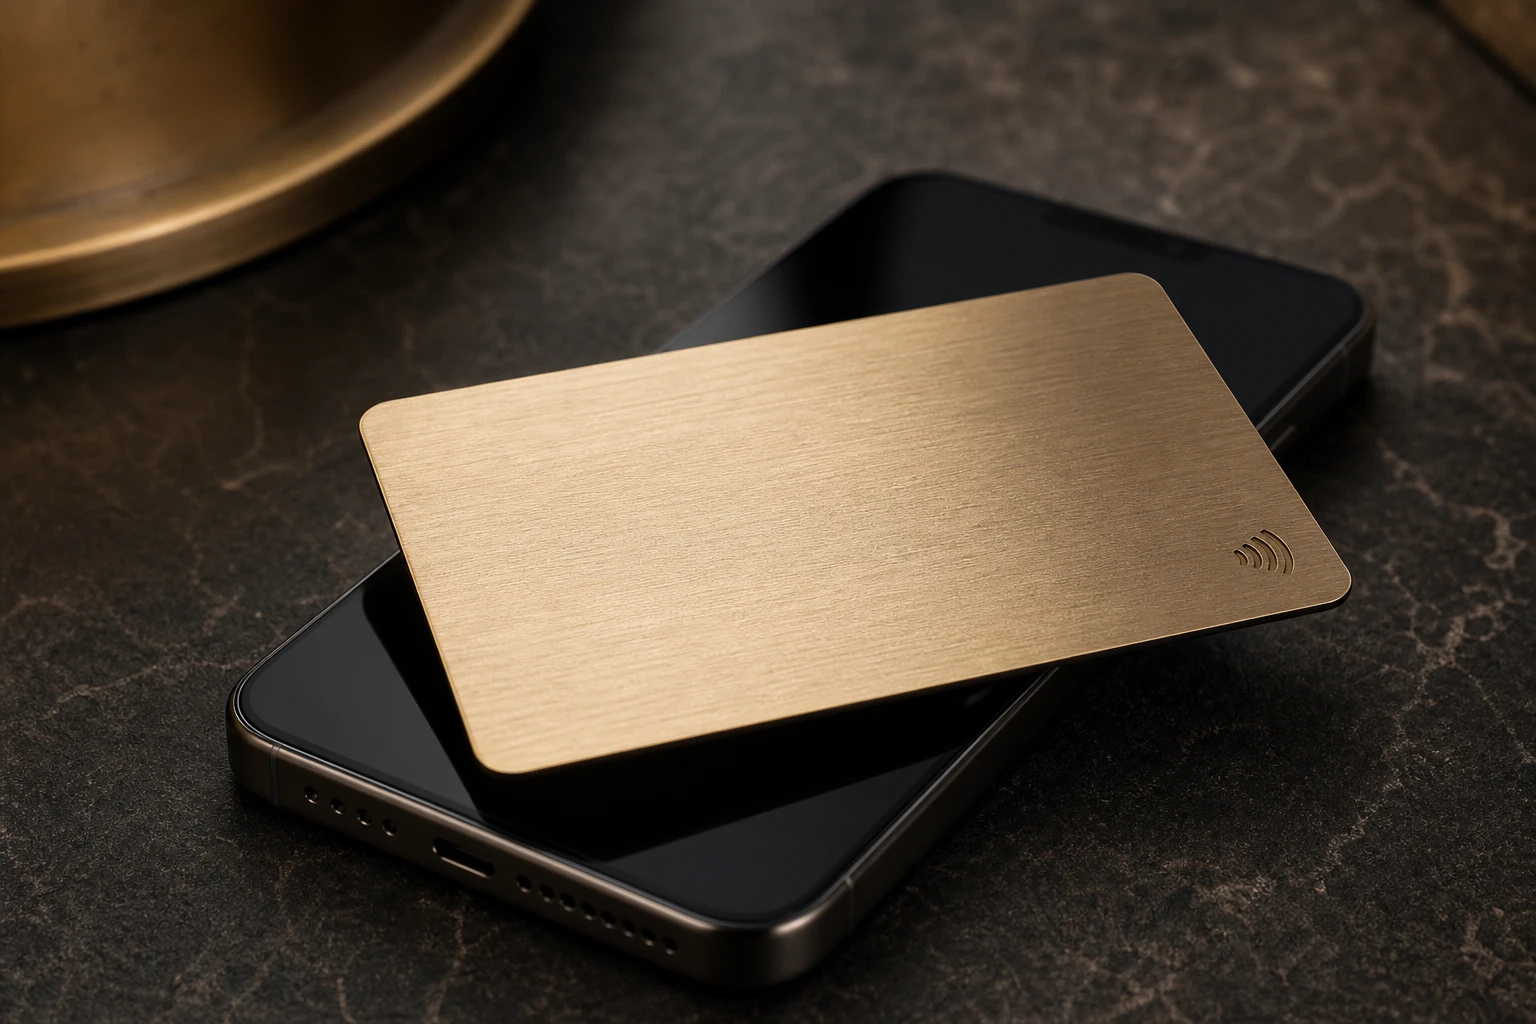
A warm premium finish can still support a reader-tested phone-tap route when the RF stack is approved first.
For standard HF, high-security AES HF, and access builds, validate a finished card on the real reader before batch approval.
A copper finish direction that preserves the same reader-first approach: shield, antenna, chip, and final surface are tested together.
Use a purpose-built test bench for 125 kHz compatibility, legacy reader behavior, and final encoded-card validation.
Long-range UHF work needs range, orientation, reader power, nearby materials, and final metal body testing.
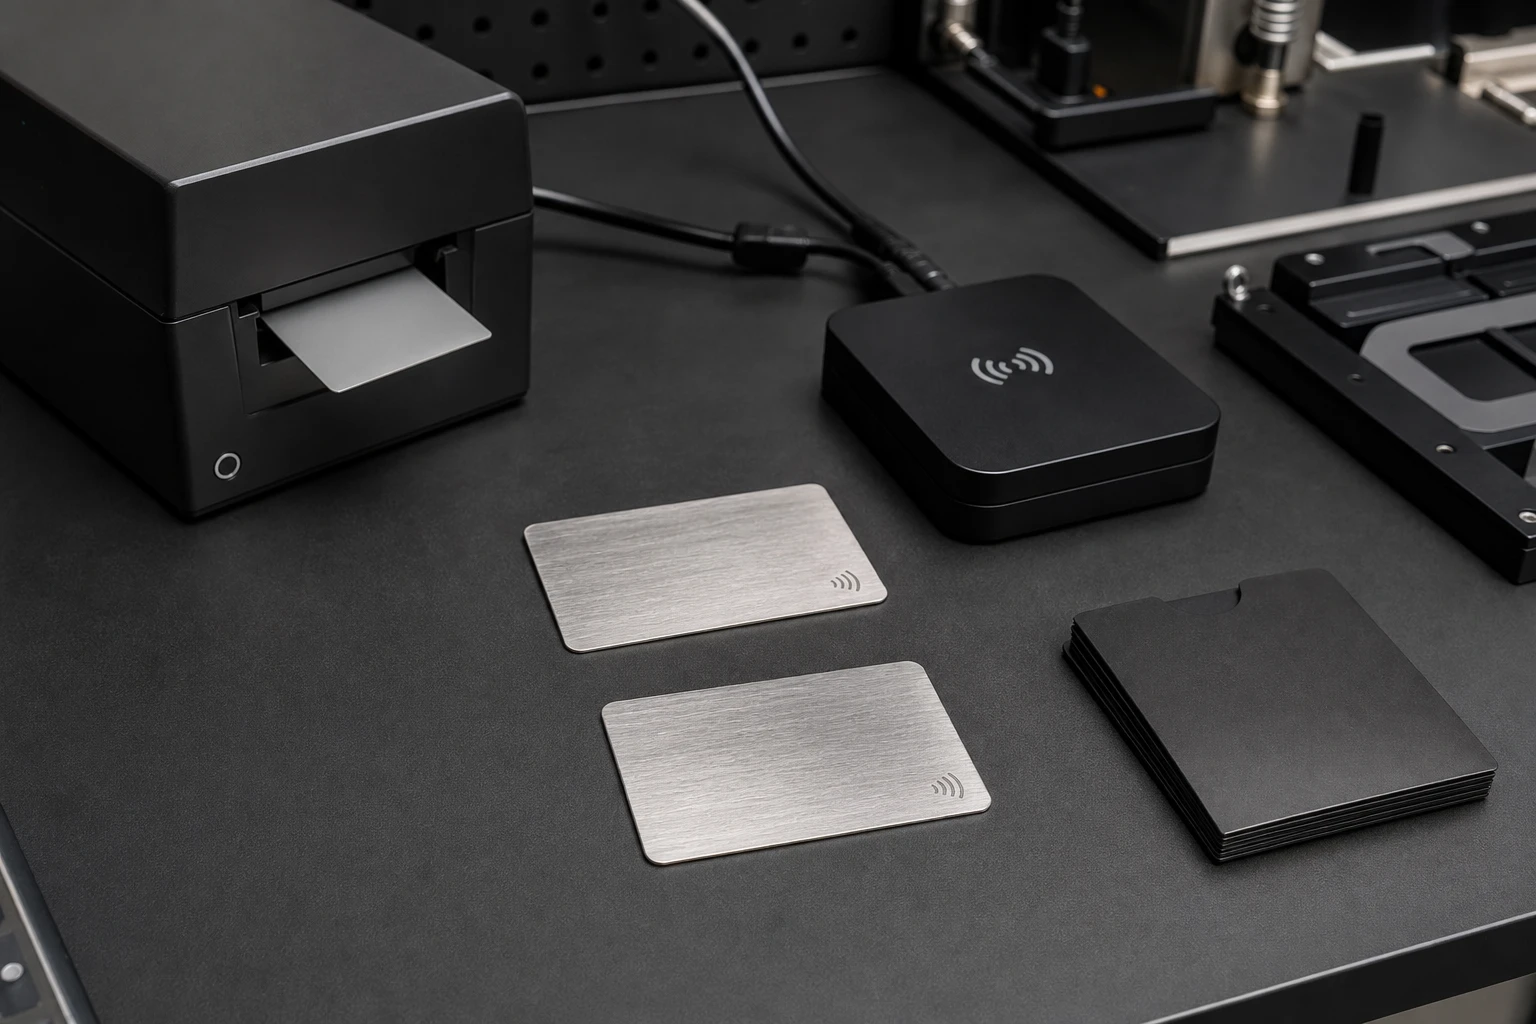
Keep UID exports, NDEF records, QR, serials, packaging labels, and card batches reconciled from one approved source file.
Use this to judge how the wood body, tap area, chip route, and reader test fit together.
The integrator owns the keys — the build follows their spec.
high-security AES HF projects run in a fixed order: the access integrator specifies chip generation, application IDs, and key handling; personalization happens under their rules; the finished metal card is then validated on the target readers. What the metal changes is the RF stack around the chip — the security model stays exactly where the integrator put it.
Approve a working sample in the real environment.
The integrator defines keys and encoding, then validates finished samples on the target reader.
(05) — Applications
Best uses for High-security AES.
The practical route is selected from the system, audience, and handling context before the final metal finish and mark treatment are approved.
Best for
- Secure enterprise, campus, premium hotel, club, and multi-application credential programs.
- Metal card programs that can validate a finished encoded sample on the target reader
- Projects that need print, serial, QR, packaging, and data handling reconciled in one approved brief
Quote details
- Target reader, lock, phone, scanner, or platform
- Metal finish, quantity, and packaging need
- Artwork files, data file, and encoding requirements
- Sample approval and delivery deadline
(06) — Specification
Production details to confirm before sample or batch.
Metal card production should confirm body construction, finish, chip route, data handling, marking layers, and approval samples in one brief.
(FAQ) — Common questions
Questions buyers ask about High-security AES.
01When does a metal card program need high-security AES HF?
When the estate requires cryptographically secure credentials or one card carrying several applications — enterprise access, campus, premium hotels, clubs with cashless spend. If the platform only checks a UID, high-security AES HF is more chip than the program needs.
02What is the difference between modern AES generations?
Both use AES-128 and the same application model; The newer generation is current, with improved performance and security certifications. In practice the integrator's platform specification decides which generation is ordered.
03Who defines the high-security AES HF encoding?
The access integrator: application IDs, file structures, and key handling are theirs. Cards are personalized under those rules and validated as finished metal samples on the target readers before the batch.
(09) — Quote High-security AES
Send quantity, chip, material, print and encoding requirements.
Engineered antenna pathFerrite or hybrid RF structureLaser and deep engravingBrushed, plated, coated finishesUID, NDEF, and access encodingSample kits and production approval